 All posts
When a Random Panel Question Nails It
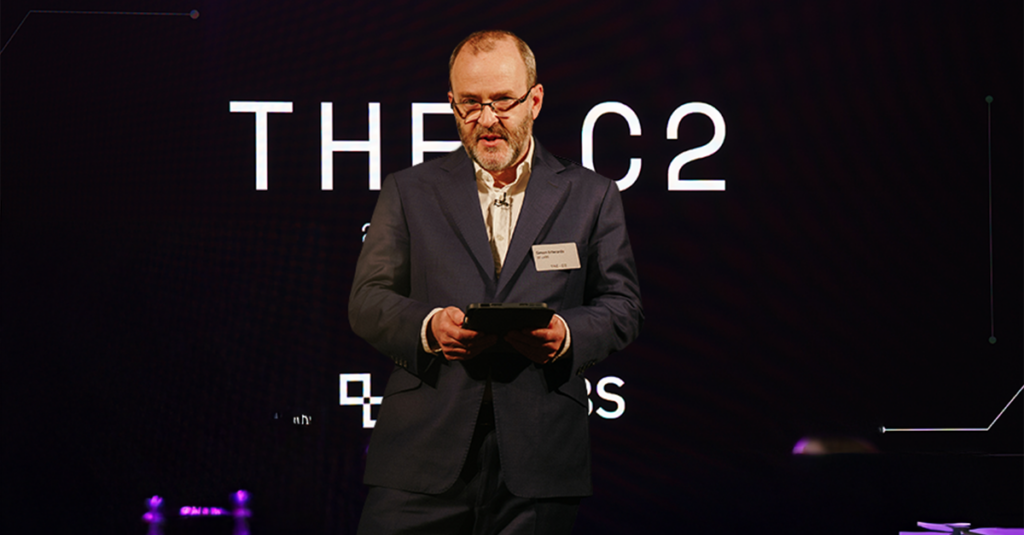
At the end of The-C2 cyber threat intelligence conference, I stood up to summarise and reflect on the talks and break-out discussions enjoyed by the delegates over the previous two days.
Initially I was going to run through each of the talks and pull out a few of the key conclusions. But something unexpected happened. There was one question that came up on the first day’s panel that really grabbed my attention. It stuck in my head, and I ended up fixating on it all evening, and again the following morning.
It’s quite a hard question to understand, on the face of it. So, I didn’t really give it much thought, at least initially. But I was sitting on the panel so I figured I should at least get to grips with it. With some effort I did my best.
The question was: “Do you believe businesses fully understand how their digital supply chains underpin national infrastructure”
The obvious answer is, “no.”
That’s accurate and we can believe it because most businesses don’t have a cyber security plan, which means they are not thinking about cyber security at all. Which also means that the level of sophistication required to visualise and understand a cyber security supply chain is clearly not there. So, no. They don’t understand.
Good Citizens Work Together
When I started writing up my notes for the closing speech of The-C2 I kept coming back to that question. Something about it bothered me. It felt almost profound. And then I realised that the question is really about what it means to be a good citizen.
By ‘good’ I mean as considered to be good in a liberal democracy. In my opinion, being good is where we look after each other rather than climbing over everyone else to score personal wins. We cooperate, in the way that has made human beings the dominant species in the world. For better or worse.
In the non-digital world we expect (and sometimes reward) good behaviour and punish bad behaviour. That really helps foster cooperation.
Culture vs. Law
‘Good’ and ‘bad’ are both cultural and legal concepts. You can do what your people expect or want; and you can follow your government’s law.
These two things do not always align.
I’ve seen enough people ignoring road crossing signs; warnings not to swim; and other examples of low-level non-compliance. I’d say that was cultural. I know people from many cultures around the world, and some are astounded by Londoners’ inability to care about traffic lights. I have personally been shocked at the difference in parental discipline shown by certain groups as I’ve travelled the world.
When you get a culture clash it jars. When someone doesn’t comply with my concept of what it means to be polite, efficient or respectful, there is friction. Cultures require members to comply with ‘normal’, or problems arise. There can be ‘tut’ moments of irritation or mob violence.
As one of The-C2 delegates said during the panel in question, we even have cultural differences when it comes to doing business. Europeans and Americans have, in his experience, quite different approaches to buying and selling. Europeans might be slower to buy, but they might stick with the product longer than a fast-buying American. That’s not very exciting insight for sales teams. It’s a bit too strategic for a salesperson who will not earn a commission for each year that the buyer stays a customer.
Good Law vs. Bad Law
We know there are countries in which people do not enjoy the same levels of freedom that we do in parts of the West. The law of those lands are repressive, we think. And when those people agree, and go against the law, there can be severe repercussions. Iran is the most obvious example in recent months. There have been plenty of others in living memory.
The law requires citizens to comply with the system. There can be formal warnings, arrests or torture.
Decency and Trust
In our society it’s generally considered that people should be responsible and contribute to the system, by paying taxes for example. Then add to that the concept of decency – such as stopping someone stepping out accidentally (or purposefully) into traffic. Noticing when someone drops a bank note and handing it back to them. Using litter (trash) bins (cans) rather than dropping rubbish in the street.
That’s not supposed to be special kindness. That’s baseline good behaviour that we were taught as children. It helps build some level of trust in our community, without which our lives would be much harder and messier.
We sometimes give to charity. That’s considered to be kindness by some, and a duty by others. Maybe larger businesses can show similar kindness to its smaller suppliers and help with the so-called ‘cyber poverty’ that affects most businesses that aren’t in the top 10%.
This is something that came up in one of The-C2’s first day’s breakout sessions and in a great pre-dinner speech on the first night. It’s a growing theme, it seems. There’s a direct self-interested benefit to this ‘charity’, so it doesn’t even have to be altruistic. It could even be tax deductible.
Joint Resilience
It’s probably necessary. The same dinner speaker made the point that resilience is not a solo effort. Humans are a successful species because we cooperate. As hackers continue to win, and AI helps them accelerate, this feels like an opportunity to exercise some of that cooperation.
The-C2, and other meetings like it, play a small part of that. But it needs to be more systemic. Probably culturally, rather than legally.
We reject terrible crimes. We are repelled by those who murder, and we avoid being murderers. For that extreme level of crime there isn’t usually any real conscious thought: “Today I must remember not to murder!”
We don’t like it and so we don’t do it. Most of us can get through a day without trying not to murder someone. It’s not the illegality of murder that stops most of us going on a spree. It’s probably a mixture of how we are brought up and how we evolved.
Herd Benefits
So back to the original point – that question about businesses and their position in the supply chain. This question implies that they have a responsibility to the greater good. Or at least to the other businesses in their immediate ecosystem. There is probably some etiquette too. What does decency look like in cyber security? Our parents and teachers didn’t coach us to install anti-virus for other peoples’ benefit. There is a whole other talk here, on the concept of herd immunity. If enough systems are hardened; if enough people behave in a certain, secure way; then it makes life much harder for the attackers overall.
Even the ignorant benefit from the wider knowledge. We all benefit.
Maybe AI can help with this. Maybe it can make small improvements to security at scale. Certainly some of the cyber security vendor companies are banking on that. Home users don’t care about ‘malware’. But they do care about scams, for example. So we’re seeing ‘anti-scam’ leading the marketing charge now, rather than ‘anti-virus’.
And while AI won’t be perfect, it’s better than what we have – which is zero knowledge for most people and businesses.
Do Your Research
There’s some classic advice that tech journalists always give to help keep you safe with your smartphones. Always install from known stores and (get this) research the product. Who is going to do that? What does that mean? To help, we published a more in-depth guide on how to research a mobile app without being a cyber security expert.
But in general, when we’re asked to do our research, we’re often left in the dark. And then later criticised for believing what we read online.
One of our speakers noted that common advice when deploying AI is to perform a risk assessment. But how? Of what, exactly? We need help. We probably need to be told what to think, many times. Or at least be given information that it’s possible to consume meaningfully.
Another speaker at The-C2 noted that we’re not built to adapt as fast as the current technology. We’ve heard that we’re looking at something like the invention of the printing press, which caused huge disruption and brought down the status quo. The danger today is that, unlike then, power won’t pass to the people but to tech oligarchs.
We’re all in it together. Technology is both powerful and dangerous. Teaching each other and adopting a sense of group responsibility might be the way we win the 21st century.
The-C2, hosted by SE Labs, is a threat intelligence conference that connects multinational business executives with the cutting edge of the cyber security industry. For more information please visit https://the-c2.com/